 Nico Triballier
12 min read


In this tutorial, we will leverage OpenID Connect (OIDC) to allow our DevOps team to securely access their EKS clusters on AWS. We use Role Based Access Control (RBAC)] to enforce the least privilege required without the need to configure AWS IAM roles. 😎
We'll highlight the steps to manually enable an OIDC provider on your EKS clusters. At the end of this tutorial, we'll point to resources you can leverage to automate all those steps.
Below is the target architecture you'll be deploying:

This tutorial is intended to show AWS DevOps and Identity Security administrator teams how to securely access Amazon Elastic Kubernetes Service (EKS) clusters. Anyone with an interest in Identity Security best practices can learn from this guide, but it assumes at least some knowledge of:
The prerequisites to complete this tutorial are:
Okta, Inc. is an identity and access management company, providing cloud software that helps companies manage and secure user authentication into applications, and for developers to build identity controls into applications, websites, web services, and devices. You get scalable authentication built right into your application without the development overhead, security risks, and maintenance that come from building it yourself.
Kubernetes, also known by the abbreviation k8s, is an open-source container orchestration platform for automating deployment, scaling, and management of containerized applications. See https://kubernetes.io/.
Amazon Elastic Kubernetes Service (Amazon EKS) is a managed container service to run and scale Kubernetes applications in the cloud or on-premises. See https://aws.amazon.com/eks/.
To deploy k8s clusters on your own infrastructure, you can use EKS Anywhere. See https://aws.amazon.com/eks/eks-anywhere/
Let's take an EKS cluster deployed in AWS. We'll perform the following steps:
id_token from Okta and passes it to our kubectl (Kubernetes command-line tool) commandsReady? Let's get started!
Let's first deploy a brand new EKS cluster. We'll do it manually from the AWS Console.
Note: We recommend configuring access to the AWS Console using Okta SSO+MFA.


Let's create a brand new EKS cluster.


Your EKS cluster will take a couple of minutes to start. In the meantime, let's do the configuration on the Okta side. Then we'll come back to the AWS Console to configure Okta as the OIDC provider for the EKS cluster.
In the Okta admin console, we'll create a group of users that we'll assign to a OIDC client, and we'll configure the AuthZ Server to inject the list of groups into the id_token.


You should see that your user is now assigned to the eks-admins group:

Now we'll create a new OIDC client. We'll leverage the AuthCode + PKCE grant type since the terminal to access EKS clusters will be running on the laptops of DevOps team members, and like any native app, it can't host any secrets.


Enter the following settings:


Enter the following settings:
Click on Save.


Now let's add a custom claim "groups" in the id_token that Okta will generate, to list the groups of the connected user.

Use the following settings to add the groups claim in the id_token:

Now let's create an access policy on this AuthZ Server to drive when the AuthZ Server should mint the id_token.

Enter the following Policy settings:


Enter the following Rule settings:
Then click on Create Rule.

You should see this view:

Now let's run a test to see what our id_token will look like when the Okta AuthZ Server mints it.
Go to the Token Preview tab and enter the following Request Properties:
Then click on Token Preview. On the right side of the screen, you'll see a preview of your id_token. So far it has all the claims we're looking for, including:

The configuration on the Okta side is complete.
Now let's get back to the AWS Console:

Enter the following parameters:
Then Save.

Note: Your EKS cluster configuration may take 5-10 minutes to update after you add the OIDC provider.
Now let's update the kubeconfig of the EKS cluster so the API server prompts for authentication whenever there's an inbound kubectl request. We'll also add an RBAC control stating that a user part of the eks-admins Okta group will have the k8s ClusterRole cluster-admin.
To update the EKS kubeconfig we'll use AWS CloudShell. It's particularly convenient to make quick updates if you access the AWS Console with Okta SSO and assume a given role, as we did earlier in this tutorial:


You should land on this view:

Let's install kubectl (source):
curl -LO "https://dl.k8s.io/release/$(curl -L -s https://dl.k8s.io/release/stable.txt)/bin/linux/amd64/kubectl"curl -LO "https://dl.k8s.io/$(curl -L -s https://dl.k8s.io/release/stable.txt)/bin/linux/amd64/kubectl.sha256"echo "$(<kubectl.sha256) kubectl" | sha256sum --checkIf valid, the output should be:

kubectlsudo install -o root -g root -m 0755 kubectl /usr/local/bin/kubectlkubectl version --client
aws eks --region us-west-1 list-clusters
kubeconfig file:aws eks --region us-west-1 update-kubeconfig --name eks-cluster
kubeconfig file looks like.kubectl config view
kubectl config current-context
sudo yum install -y nanoCreate a cluster role binding:
nano oidc-cluster-admin-by-group.yamlkind: ClusterRoleBinding
apiVersion: rbac.authorization.k8s.io/v1
metadata:
name: oidc-cluster-admin
roleRef:
apiGroup: rbac.authorization.k8s.io
kind: ClusterRole
name: cluster-admin
subjects:
- kind: Group
name: eks-admins
kubectl create -f oidc-cluster-admin-by-group.yamlkubectl apply -f oidc-cluster-admin-by-group.yamlnano $HOME/.kube/config
Below is the text to include:
- name: oidc
  user:
    exec:
        apiVersion: client.authentication.k8s.io/v1beta1
        args:
        - oidc-login
        - get-token
        - --oidc-issuer-url=https://nico-okta.login.adsbillinghub.com/oauth2/auscierlvzfBoWkKC2p7
        - --oidc-client-id=0oacieu408ExEjXwu2p7
        - --oidc-extra-scope=email
        - --oidc-extra-scope=offline_access
        - --oidc-extra-scope=profile
        - --oidc-extra-scope=openid
        command: kubectl
This basically specifies the config of the OIDC provider. Note: Replace the oidc-issuer-url and oidc-client-id with Issuer URL and Client ID we copied earlier.
Once you're done editing the file:
At this point the EKS cluster is properly configured to use Okta as an OIDC provider.
From CloudShell, we can retrieve the list of pods in our cluster with our current assumed role.
kubectl get pods --all-namespaces
Let's now look into how we can run a similar command from the terminal on our local machine.
There are two things we need to configure:
Export the kubeconfig file and import it to your laptop.
Configure a kubectl OIDC plugin to prompt the user for AuthN and request an id_token. We'll use kubelogin.
From your CloudShell, enter the command:
echo $HOME
The path to our kubeconfig file is /home/cloudshell-user/.kube/config, as shown above.

kubeconfig file and click on Download.
You should now have a copy of the config file in your Downloads folder.
Install kubectl on your local machine. (See the instructions to install kubectl on macOS).
Double-check that kubectl is properly installed.
kubectl version --client
On your Mac, replace the existing kubeconfig file with the one you downloaded from CloudShell:
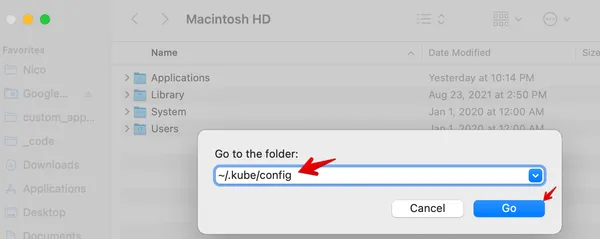

kubectl config get-contexts
kubectl config use-context arn:aws:eks:us-west-1:013353681016:cluster/eks-clusterYou may want to adjust the context name in the above command based on the context name in your own config file.
You may want to adjust the context name in the above command based on the context name in your own config file.
You may want to adjust the context name in the above command based on the context name in your own config file.
kubectl config get-contextsbrew install int128/kubelogin/kubeloginoidc-issuer-url and oidc-client-id with your own values.):kubectl oidc-login setup --oidc-issuer-url=https://nico-okta.login.adsbillinghub.com/oauth2/auscierlvzfBoWkKC2p7 --oidc-client-id=0oacieu408ExEjXwu2p7You should be prompted to authenticate in your web browser against your Okta org.


You can close this tab.
Check your terminal. You should see a confirmation that you've received an id_token from Okta:

kubectl --user=oidc get pods --all-namespacesIf you're not already Okta-authenticated you'll be prompted for AuthN. You should be able to see your list of pods:

Congratulations! You've successfully configured Okta as an OIDC provider to access your EKS cluster! 🎉
Let's double-check that our RBAC controls are working as expected. Currently we're a member of the eks-admins Okta group in the Universal Directory.

Then, let's delete the cached id_token on our laptop.
cd ~/.kube/cache/oidc-loginls
id_token Okta minted. Let's delete it.rm 8ead66f63afa81d7300257989c391d035f386b80758a2847c99d37ecdd5610e0ls
kubectl --user=oidc get pods --all-namespaces
As expected, we're not authorized. Since we're no longer a member of the eks-admins Okta group, the group is no longer injected in the id_token, and the Kubernetes API Server no longer applies the cluster-admin role.
id_token in the ~/.kube/cache/oidc-login folder.We should now be able to access the list of pods as before:

Pretty cool right? 😎
All the manual steps in this tutorial can be automated:
You successfully configured Okta as a third party OIDC provider on your EKS cluster, and applied RBAC to enforce least privilege without the need to configure AWS IAM roles. This allows you to have a very generic AuthN/AuthZ framework, for all your Kubernetes (k8s) clusters, regardless of where they run (public cloud, private cloud, or on-prem).
To learn more about OAuth 2.0 and OIDC, check out these blog posts
Follow Okta Developers for more great content and updates from the team! You can find us on Twitter, Facebook, subscribe to our YouTube Channel, or start the conversation below.
Okta Developer Blog Comment Policy
We welcome relevant and respectful comments. Off-topic comments may be removed.